Control access and keep architecture changes traceable
Manage organization-scoped roles, controlled write access, access requests, and an audit trail.
What works today
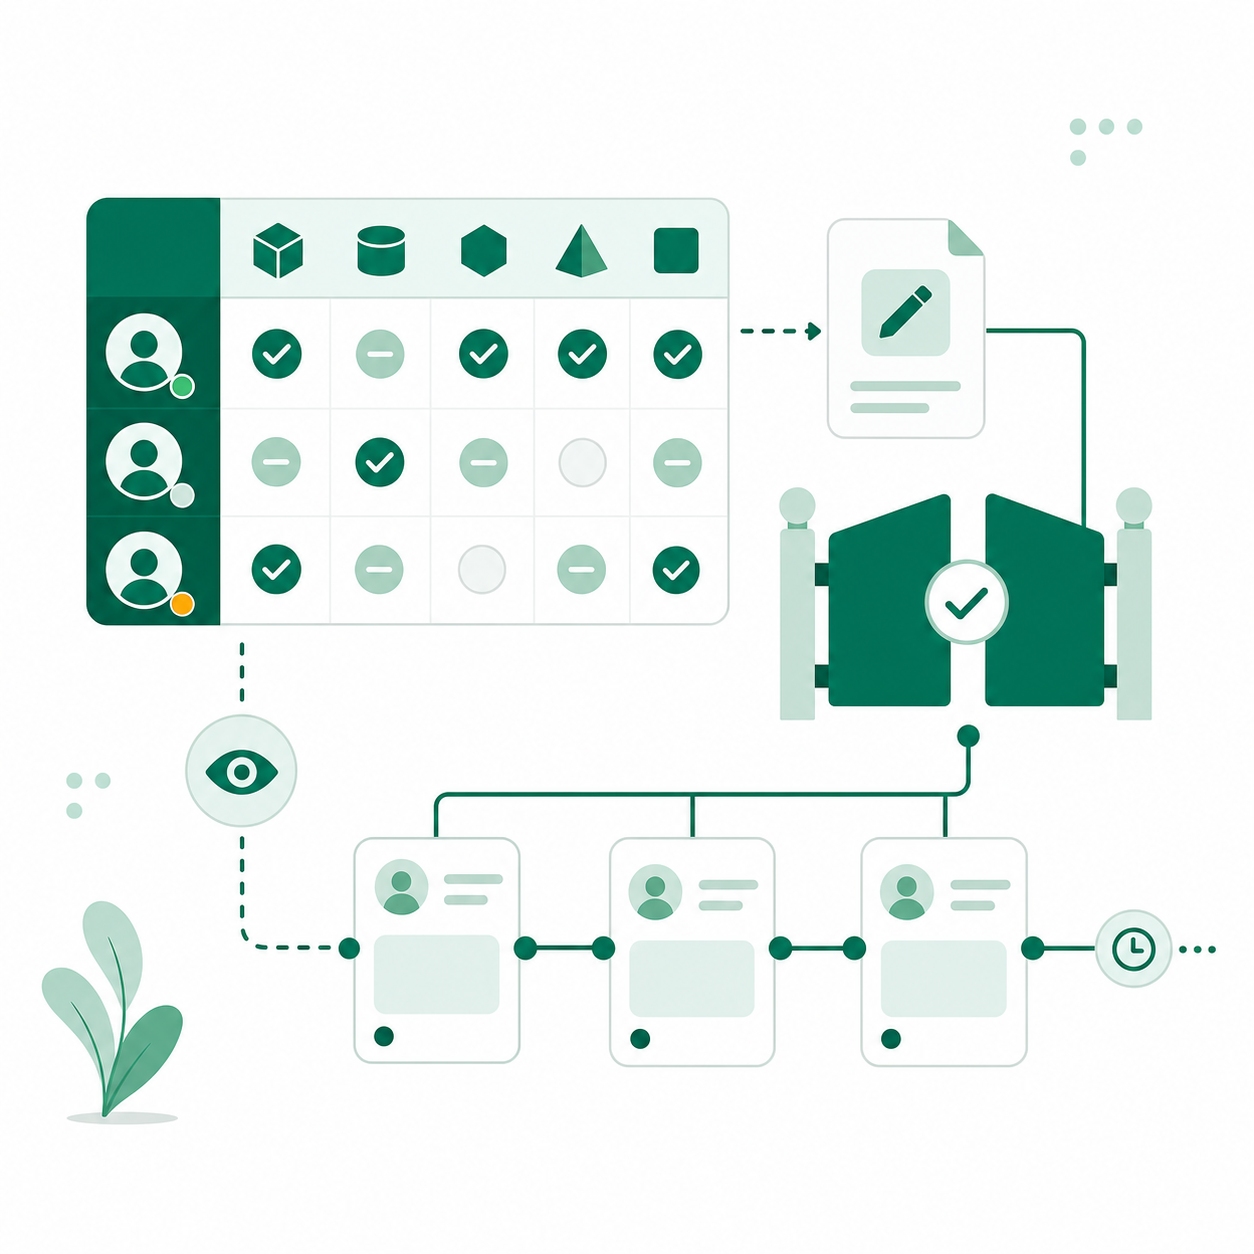
Organization-scoped RBAC
Role templates and access requests
Controlled write access
Audit trail
Key capabilities
Organization-scoped RBAC
User permissions follow their role in the organization
Role templates and access requests
Standard permission sets and access requests reviewed by an administrator
Controlled write access
Only authorized people can change data
Audit trail
A history of who changed what and when
Enterprise sign-in (SAML) and MFA
Coming soonSign in through your corporate identity provider over SAML, with multi-factor authentication
Automated data-classification enforcement
Coming soonAutomatic access restrictions based on data sensitivity
What you get
Permissions granted by role, not person by person
Access granted on request, with review
Only authorized people make changes
Architecture changes are recorded in the audit trail
ArchPad in action
What works today
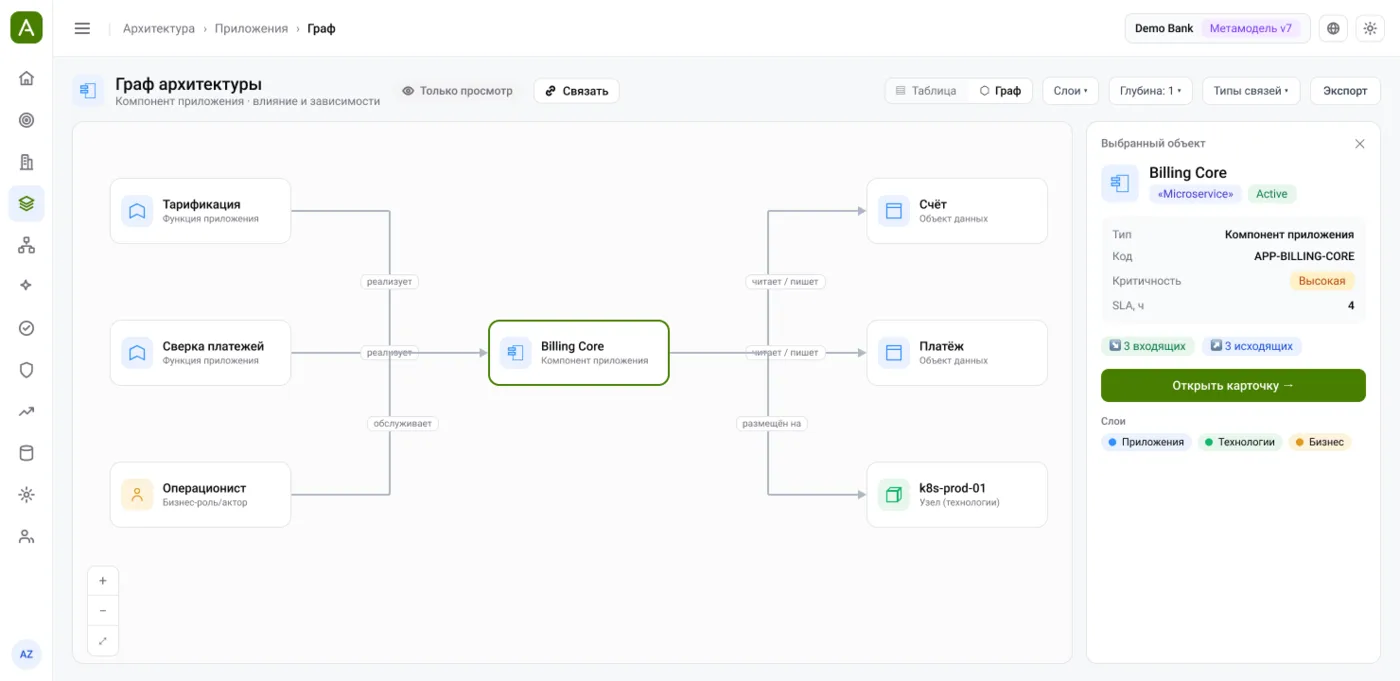
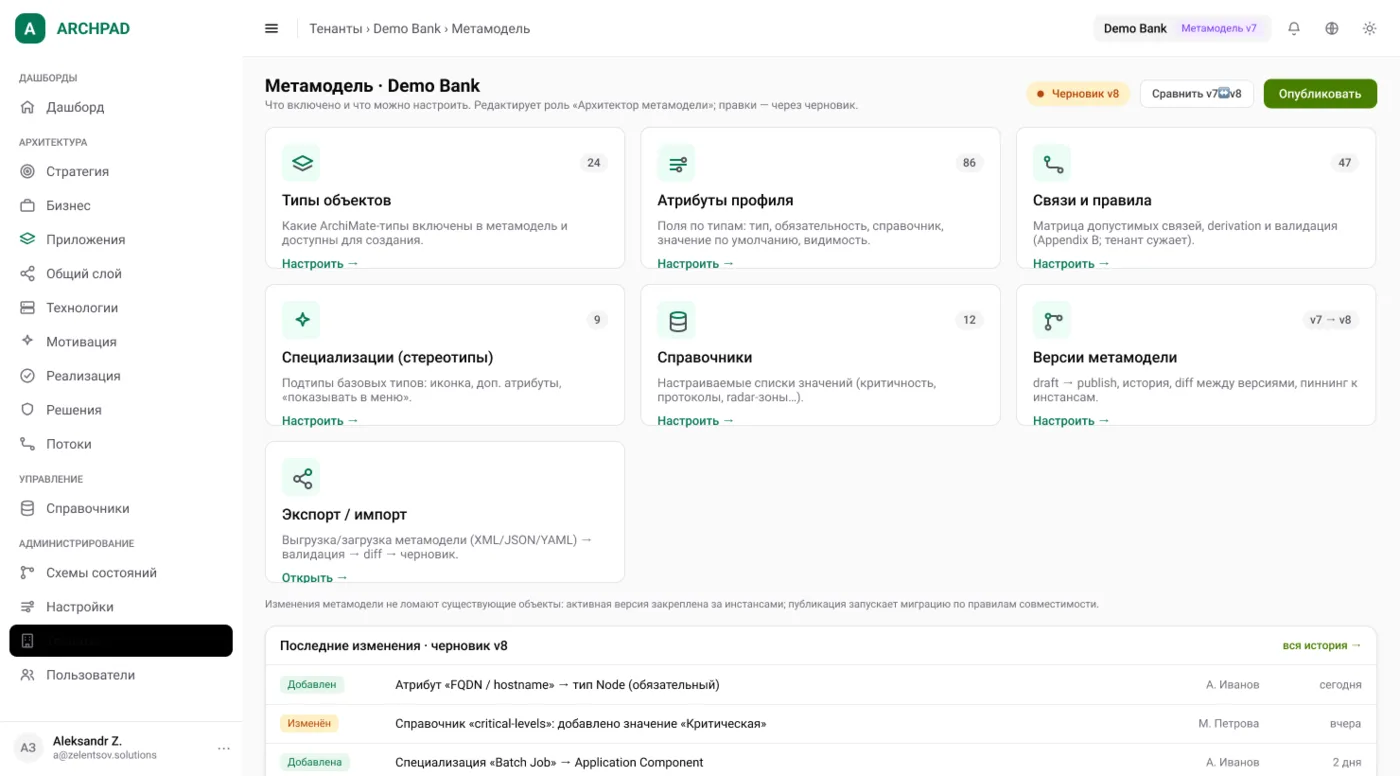
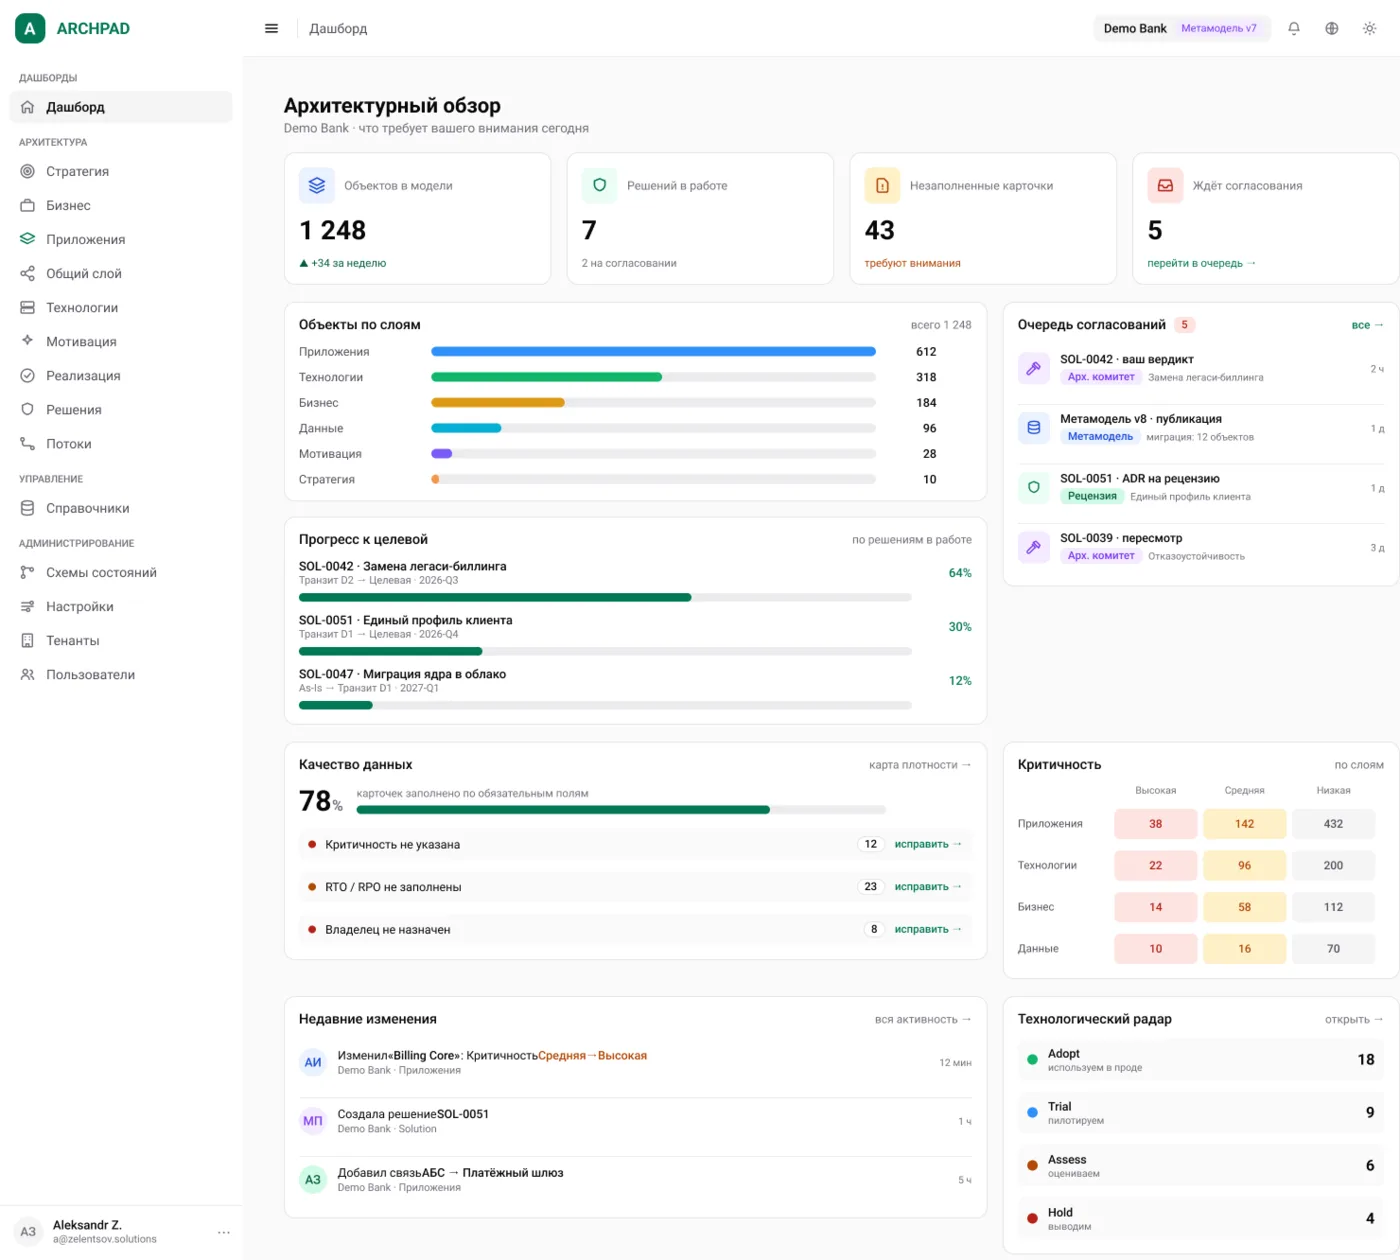
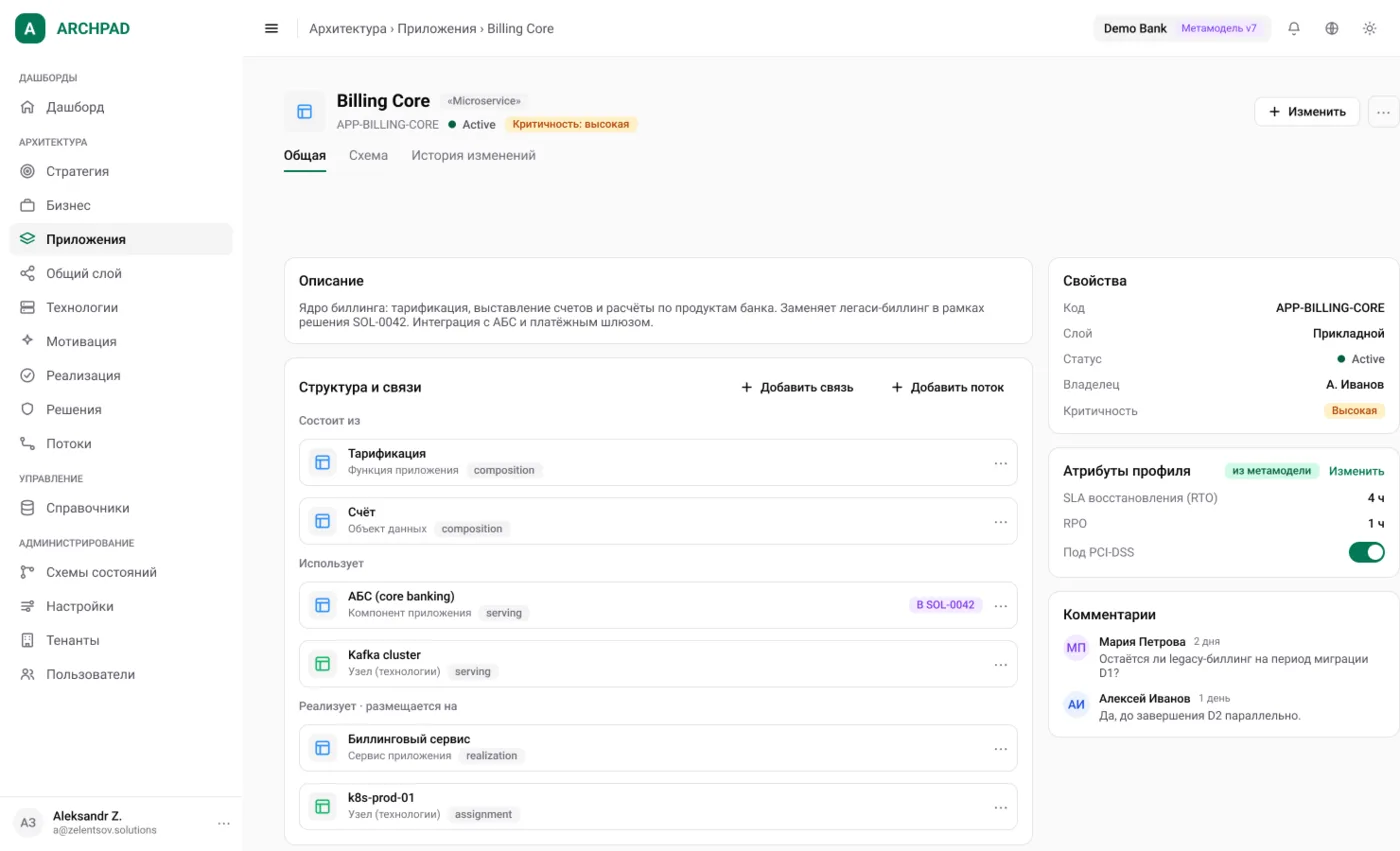
Keep architecture access controlled and traceable
Create an account to try access control and audit
- Configurable metamodel
- Dependency graphs and impact context
- Governance and portfolio dashboards
- Organization-scoped roles and audit